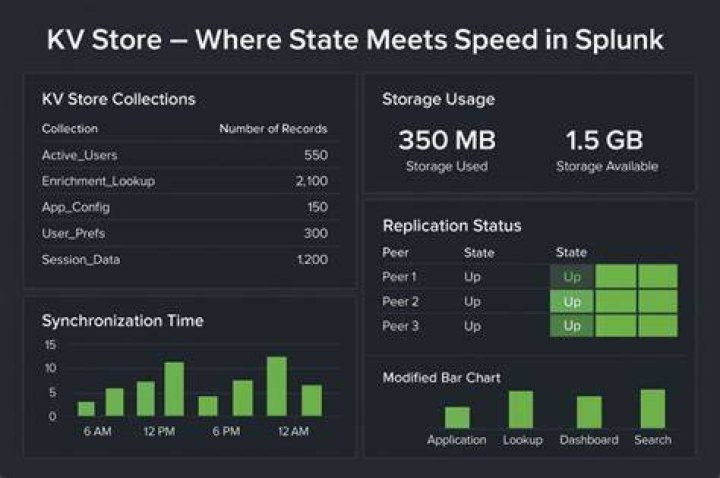
What is Splunk KV store?
 John Peck
Subsequently, one may also ask, how do you make a KV store in Splunk?
- Select Settings > Lookups.
- Click Lookup definitions.
- Click Add new.
- Change the Type to KV Store.
- Enter the collection name to use as defined in collections.
- List all of the fields that are supported by the KV Store lookup.
- (Optional) Configure time-based lookup.
Also Know, what port does Splunk use? The DCN uses port 443 to determine the kind of data to collect, such as performance, inventory, or hierarchy data. Splunk App for VMware sends information to the data collection nodes using port 8008 about the information they need to collect from a specific vCenter Server system.
One may also ask, what is lookup table in Splunk?
A lookup table is a mapping of keys and values. Splunk Lookup helps you in adding a field from an external source based on the value that matches your field in the event data.
What is key value data store?
A key-value database, or key-value store, is a data storage paradigm designed for storing, retrieving, and managing associative arrays, and a data structure more commonly known today as a dictionary or hash table.
How do key value stores work?
A key-value store is a database which uses an array of keys where each key is associated with only one value in a collection. Also the key-value stores usually do not have query languages as in RDBMS to retrieve data. They only provide some simple operations such as get, put and delete.How do I create a splunk lookup table?
- From the Search app, then select Settings > Lookups.
- Select Add new for Lookup table files.
- Select search for the destination app.
- Browse for the CSV file that you downloaded earlier.
- Name the lookup table http_status.
- Click Save.
What is a lookup file?
A Lookup file is a two-dimensional table of data that has been stored in a disk file. A name and display format for each column of data may also be stored, depending on the file format.How do I edit a lookup table in Splunk?
Currently, to edit a lookup table we do the following.- Run an inputlookup search on the file and export it to Excel.
- Edit the table in Excel and save it locally.
- From the Splunk manager, delete the existing lookup table.
- Upload the edited version.
- Set the permissions so that all can use it.
How do I read a csv file in Splunk?
A Graphical User Interface for Editing and Importing FilesTo do so, open the Lookup Editor and click the “New” button. Next, click “import from CSV file” at the top right and select your file. This will import the contents of the lookup file into the view. Press save to persist it.How do I upload a lookup file to Splunk?
To use a lookup table file, you must upload the file to your Splunk platform.- In the Lookups manager, locate Lookup table files and click Add new.
- The Destination app field specifies which app you want to upload the lookup table file to.
- Under Upload a lookup file, click Choose File and browse for the prices.
Does Splunk use TCP or UDP?
Splunk Enterprise supports monitoring over UDP, but you should use TCP to send network data instead whenever possible. UDP is not desirable as a transport because, among other reasons, it does not guarantee delivery of network packets.What is Splunk used for?
Splunk is a software mainly used for searching, monitoring, and examining machine-generated Big Data through a web-style interface. Splunk performs capturing, indexing, and correlating the real-time data in a searchable container from which it can produce graphs, reports, alerts, dashboards, and visualizations.Is Splunk free to use?
Splunk Free is the totally free version of Splunk software. The Free license lets you index up to 500 MB per day and will never expire. The 500 MB limit refers to the amount of new data you can add (we call this indexing) per day. But you can keep adding data every day, storing as much as you want.What are the three main processing components of Splunk?
There are 3 main components in Splunk:- Splunk Forwarder, used for data forwarding.
- Splunk Indexer, used for Parsing and Indexing the data.
- Search Head, is a GUI used for searching, analyzing and reporting.


