2 Answers. Yes, there are currently no known attacks on HMAC-MD5. "Abstract: HMAC was proved by Bellare, Canetti and Krawczyk (1996) to be a PRF assuming that (1) the underlying compression function is a PRF, and (2) the iterated hash function is weakly collision-resistant.Moreover, is Hmac secure?
As denoted by its name, HMAC is still a hash, but a cryptographically secure one. To make it cryptographically secure usually I recommend using SHA-256 (secure hash algorithm) or stronger.
One may also ask, what is HMAC secret? HMAC stands for Keyed-Hashing for Message Authentication. It's a message authentication code obtained by running a cryptographic hash function (like MD5, SHA1, and SHA256) over the data (to be authenticated) and a shared secret key. HMAC is specified in RFC 2104. They both use cryptographic keys.
Regarding this, how is using HMAC more secure than general hashing?
What makes HMAC more secure than MAC is that the key and the message are hashed in separate steps. It can also be proven secure based on the cryptographic strength of the underlying hash function, the size of its hash output length and on the size and strength of the secret key used.
What is the difference between Mac and HMAC?
The main difference between MAC and HMAC is that MAC is a tag or a piece of information that helps to authenticate a message, while HMAC is a special type of MAC with a cryptographic hash function and a secret cryptographic key.
Is Hmac a digital signature?
What is an HMAC signature? An HMAC (Hash-based Message Authentication Code) signature is a form of a digital signature. HMAC signatures start with a secret key that is shared between the sender (DocuSign Connect) and the recipient (your application's listener server).Does sha256 need a key?
The definition of a hash function is a map from a single input to an output. Hash functions like SHA-* do not need a key, they just calculate a hash-value from any input. There are other functions like HMAC, which indeed use a key, together with a hash function.What are two symmetric encryption algorithms?
Blowfish, AES, RC4, DES, RC5, and RC6 are examples of symmetric encryption. The most widely used symmetric algorithm is AES-128, AES-192, and AES-256. The main disadvantage of the symmetric key encryption is that all parties involved have to exchange the key used to encrypt the data before they can decrypt it.Do we have to use a key with a fixed size in Hmac?
Keys. The key for HMAC can be of any length (keys longer than B bytes are first hashed using H). Keys longer than L bytes are acceptable but the extra length would not significantly increase the function strength. (A longer key may be advisable if the randomness of the key is considered weak.)Is Hmac reversible?
1 Answer. Actually the HMAC value is not decrypted at all. You can roughly see the HMAC algorithm as an symmetric key signature. You cannot decrypt an HMAC, you only check that the value is correct.Why do we need Hmac?
Hash-based message authentication code (HMAC) is a mechanism for calculating a message authentication code involving a hash function in combination with a secret key. This can be used to verify the integrity and authenticity of a a message.How do I get the HMAC key?
First, enter the plain-text and the cryptographic key to generate the code. Then, you can use select the hash function you want to apply for hashing. The default is SHA-256. Then you can submit your request by clicking on the compute hash button to generate the HMAC authentication code for you.Does Mac provide confidentiality?
Encryption provides confidentiality, a MAC provides integrity. Using encryption alone makes your messages vulnerable to a ciphertext only attack. The sender, with the symmetric key, can encrypt the message and send E(M) . You have confidentiality covered.What is meant by hashing?
Hashing is generating a value or values from a string of text using a mathematical function. Hashing is also a method of sorting key values in a database table in an efficient manner.What is md5 authentication?
The MD5 hashing algorithm is a one-way cryptographic function that accepts a message of any length as input and returns as output a fixed-length digest value to be used for authenticating the original message.Where is Hmac used?
Hash-based message authentication codes (or HMACs) are a tool for calculating message authentication codes using a cryptographic hash function coupled with a secret key. You can use an HMAC to verify both the integrity and authenticity of a message. HMAC objects take a key and a HashAlgorithm instance.Is it necessary to recover the secret key in order to attack a MAC algorithm?
It is not necessary to recover a secret key in order to perform attack on the Message Authentication Code (MAC) because, if a message is encrypted with number of keys (n), the opponent does not know which key is used by sender. On the average, 2(n-k) keys are produces perfect match.How do I decrypt Hmac?
HMAC is a MAC/keyed hash, not a cipher. It's not designed to be decrypted. If you want to encrypt something, use a cipher, like AES, preferably in an authenticated mode like AES-GCM. The only way to "decrypt" is guessing the whole input and then comparing the output.What is sha256 encryption?
SHA-256 Cryptographic Hash Algorithm. A cryptographic hash (sometimes called 'digest') is a kind of 'signature' for a text or a data file. SHA-256 generates an almost-unique 256-bit (32-byte) signature for a text.What is Hmac in networking?
HMAC Algorithm in Computer Network. HMAC algorithm stands for Hashed or Hash based Message Authentication Code. It is a result of work done on developing a MAC derived from cryptographic hash functions. HMAC consists of twin benefits of Hashing and MAC, and thus is more secure than any other authentication codes.How Mac and HMAC uses hash function encryption for authentication?
A message authentication code (MAC) is similar to a cryptographic hash, except that it is based on a secret key. She can then encrypt the message plus the HMAC using a secret key she shares with Bob. When Bob decrypts the message and calculates the HMAC, he will be able to tell if the message was modified in transit.What is sha1 used for?
SHA-1 (short for Secure Hash Algorithm 1) is one of several cryptographic hash functions. SHA-1 is most often used to verify that a file has been unaltered. This is done by producing a checksum before the file has been transmitted, and then again once it reaches its destination. 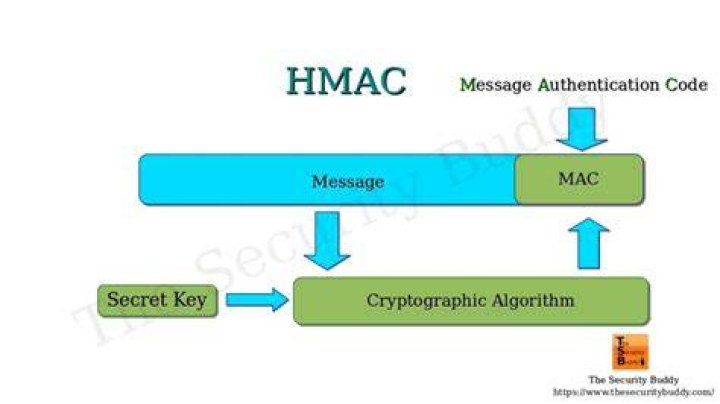
 James Austin